
Services
Kasper & Oswald GmbH analyzes and develops embedded systems with a focus on security. Many of our analysis methods come from our own research and are refined as we go.
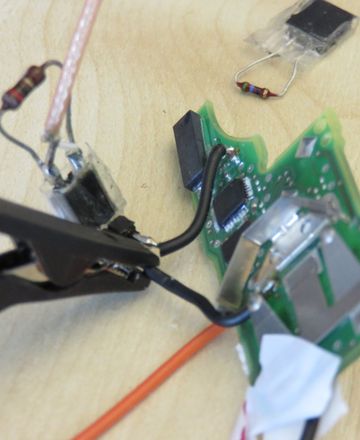
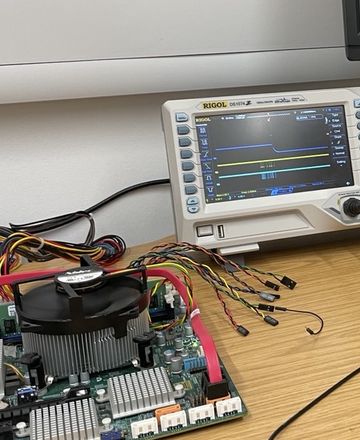
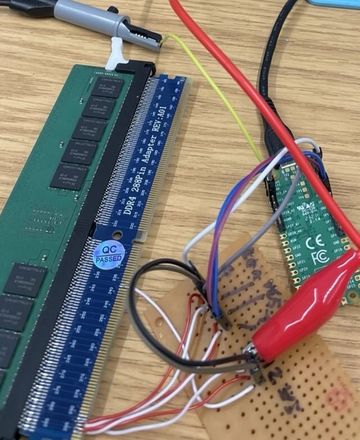
Security Analyses and Penetration Testing
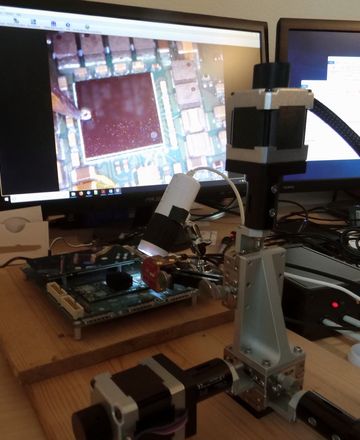
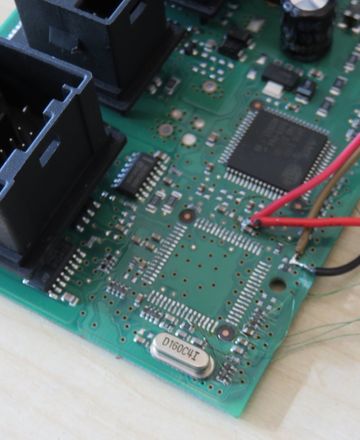
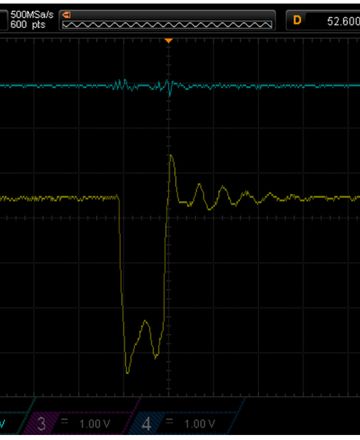
We check whether cryptographic and security-relevant functions hold up against an attacker who has the device in hand. Besides classical penetration testing, we use side-channel analysis and fault injection via voltage, clock or EM glitches, and we extract and analyze firmware. Typical targets are:
- Microcontrollers and SoCs, e.g. Espressif ESP32, STM32, Nordic nRF52/nRF54, NXP LPC and i.MX, Microchip PIC and AVR, Infineon AURIX/TriCore
- Contactless (NFC) and conventional smartcards, RFID tokens
- Security ICs (secure elements, TPMs)
- FPGAs (AMD/Xilinx, Intel/Altera) and ASICs
- IoT devices, smart meters and alarm systems
- Electronic access control and locking systems
- Hard drive and USB media encryption
Consulting
Do you need support when designing your system or evaluating its security? Kasper & Oswald GmbH advises you on hardware design and its security as well as on the design of the overall system and backend. We help you assess recent research results and regulatory requirements and take them into account during development, so that your system is secure by design.
Current Focus Areas
Automotive and Type Approval
Since July 2024, the EU requires evidence according to UN R155 (cyber security management system) and UN R156 (software updates) for the type approval of new vehicles. We test ECUs, car keys, immobilizers, telematics units and charging equipment on hardware and firmware level. The results feed directly into your TARA according to ISO/SAE 21434 and into the documents for the technical service. We have also published our own research on remote keyless entry systems.
Bluetooth and Wireless Protocols
We analyze and design wireless protocols such as Bluetooth Classic and Low Energy, UWB, NFC or proprietary protocols in the 433 and 868 MHz bands. Using software-defined radios and our own hardware, we test pairing and encryption and check whether replay or relay attacks are possible. If you are developing a new protocol, you can bring us in at the design stage.
Firmware Update and Secure Boot
We review and design bootloaders, signature schemes for (OTA) updates, rollback protection and the management of the keys involved. We also test whether debug interfaces such as JTAG and SWD and the chip’s readout protection are actually locked, or whether fault injection gets around them.
AI Hardware Security
AI accelerators, GPUs and edge AI devices run models that were expensive to train. We investigate whether the model weights can be read out via side channels or debug access, and whether fault injection can change a model’s outputs. On server platforms we also evaluate trusted execution environments and confidential computing.
Post-Quantum Security
A sufficiently large quantum computer would break RSA and elliptic curves. Devices that come to market today and stay in the field for a long time therefore need a migration path. We help you take stock of the cryptography in use and plan hybrid transition schemes. We implement the standardized schemes ML-KEM, ML-DSA, SLH-DSA and LMS/XMSS on small microcontrollers too, and test such implementations for side channels and susceptibility to faults.
Cyber Resilience Act (CRA)
The Cyber Resilience Act sets mandatory security requirements for almost all products with digital elements sold in the EU. Actively exploited vulnerabilities have to be reported since September 2026, and the remaining obligations apply from December 2027. We carry out gap analyses and risk assessments, perform the security tests needed as evidence, and support you with technical documentation, SBOM and vulnerability handling. This way you are prepared for the conformity assessment.
Hardware and Software Engineering
Kasper & Oswald GmbH designs hardware modules and embedded systems specifically tailored to your requirements. We implement security functions and cryptography efficiently and hardened against implementation attacks. We also have many years of experience in the design of digital and analog circuits. One example is the ChameleonMini, which we developed.
- Hardware and software design of microcontroller circuits, e.g. ESP32, STM32, Nordic nRF, Microchip PIC/AVR and Infineon AURIX/TriCore
- Secure bootloaders and update mechanisms
- Circuit design and VHDL development for FPGA modules
- Radio frequency amplifiers (HF), audio-frequency amplifiers (LF), filter circuits and antennas
- RFID, NFC and Bluetooth modules
- Implementing classical and post-quantum cryptography in assembly, C, C++ and VHDL
Talks, Trainings and Workshops
In our talks we present recent topics from IT and embedded security at a level of technical detail suited to your audience. They are often based on case studies from our current research. If desired, we demonstrate the described attacks live. In workshops and trainings we teach your team the basics of IT security (e.g. encryption, standards, CRA) as well as modern attack methods (e.g. side-channel analysis and fault injection). We can come to you or organize another venue. Contact us.